A CCTV clip is not a complete evidence handover merely because it plays on the recorder. The receiving team needs the original export, interpretable time information, a usable playback path and a record of what happened to the files. Plan that handover before an urgent incident makes missing metadata hard to recover.
Table of Contents
What must survive the export?
Preserve the recorded content, its identifying context and the information needed to interpret time. Also preserve the distinction between what the system recorded and what an operator later converted, annotated or redacted.
NIST’s CCTV Digital Video Export Profile recommendation, Revision 1, addresses export interoperability, time metadata and digital-signature capabilities. It provides a useful technical basis for asking suppliers about export behavior. It is not a guarantee that a particular file, product or case satisfies legal evidentiary requirements.
Before an incident, agree who may export, which cameras and time interval are needed, and how the recipient will receive and review the material. Do not rely on a screenshot of a timeline to convey the recording’s full time context.
Keep the preservation copy separate from viewing copies
Retain the native or agreed preservation export together with its associated metadata and required supporting files. If the package needs a player, record the player version and obtain it through an approved, trusted route. Avoid instructing recipients to install unexplained executables merely because a folder contains one.
A viewing copy may be useful for routine review, but conversion can change encoding, image dimensions, frame timing, audio or metadata. Give that copy a distinct name and record the operation. Redaction and annotation should likewise produce identifiable derivatives rather than overwrite the preservation copy.
NIST’s digital video exchange work identifies conversion-related quality and metadata problems as an interoperability concern. Include a representative export test in system acceptance, not just live viewing.
How do hashes and signatures differ?
A cryptographic hash summarizes file content for comparison. If a transferred file produces the expected hash, that supports a check that its contents match the version for which that trusted value was recorded. It does not independently authenticate the camera, prove the capture time or establish that the scene was genuine.
A digital signature can add a relationship to a signing key, subject to a successful verification and trust in that key. Record the verification result and relevant trust information; a visible “signed” icon is not a complete verification record.
Use the organization’s accepted integrity tools and handling procedure. Calculate values at defined points, retain the resulting manifest securely and verify the transfer. If both a file and its only hash record can be replaced unnoticed, the comparison has limited evidentiary value.
Test playback outside the recording system
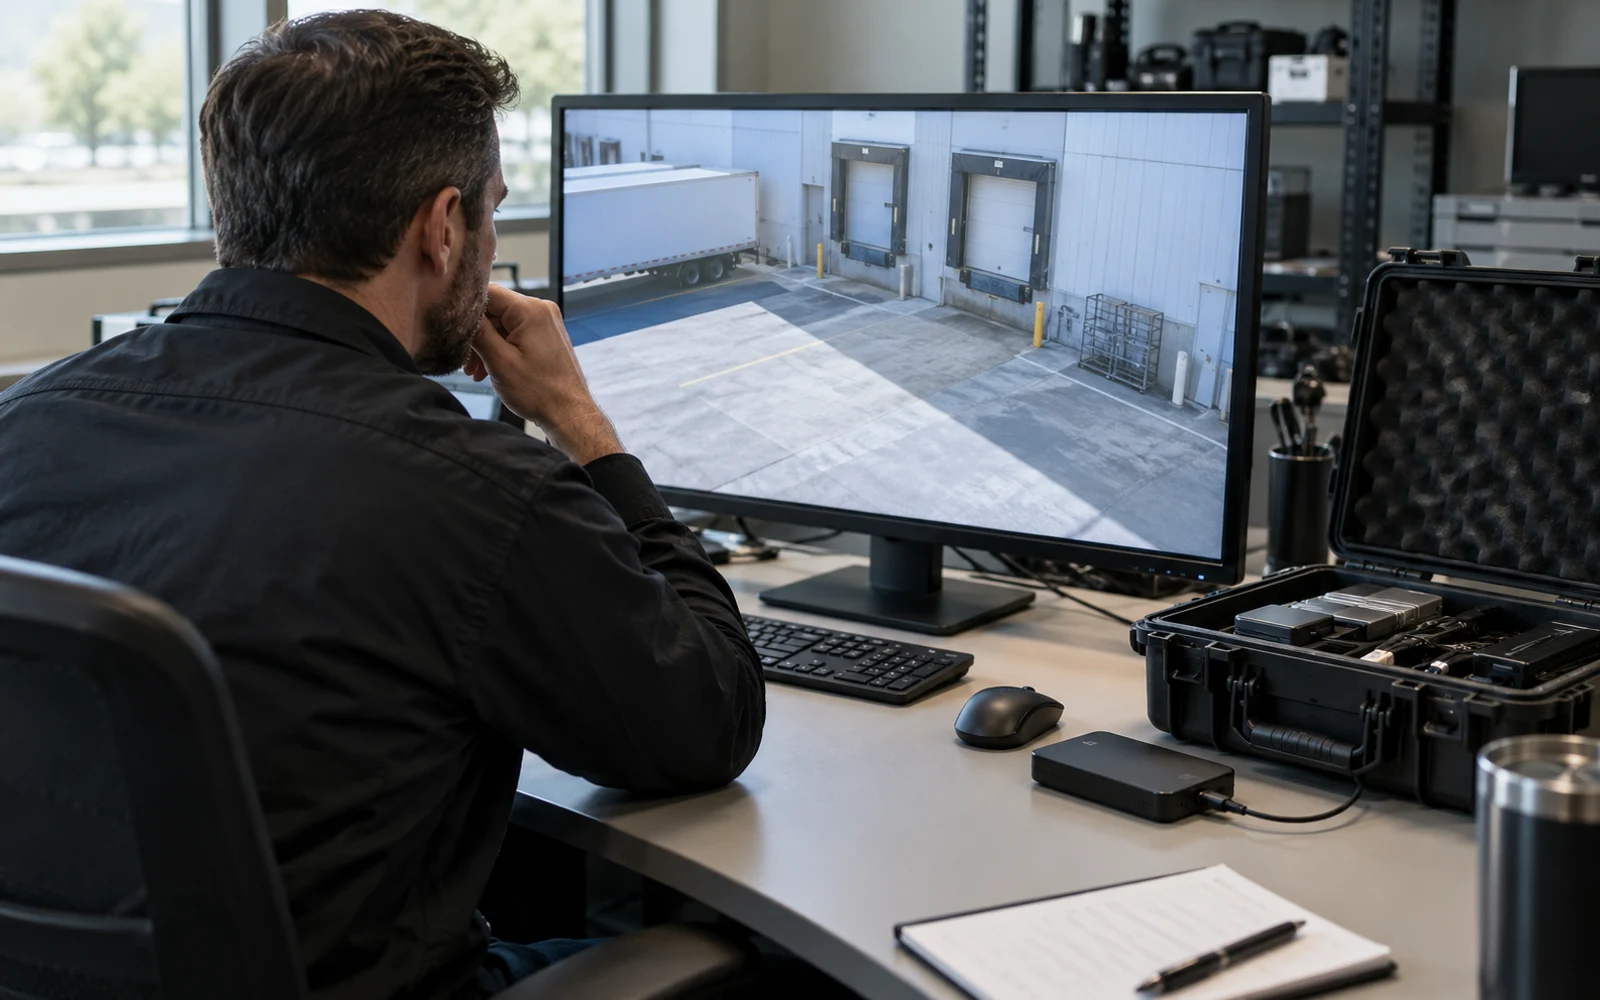
Ask an authorized reviewer to open a representative package on the intended receiving environment. Check the start and end, camera identity, continuity, expected audio, time interpretation and any multi-camera navigation.
Test the event boundaries, not only a few seconds from the middle. A successful export message does not prove that the requested lead-in or follow-up period was available. Distinguish unavailable recording, an operator’s selection and a playback failure in the report.
Include time-zone and clock-offset context where known. The camera time-synchronization guide addresses how to assess the underlying timeline. Export cannot retroactively correct an undocumented source clock, so preserve that uncertainty rather than changing timestamps without explanation.
A platform replacement adds a broader task: the video-management migration plan preserves historical search, identity and retention alongside playable files.
A handover manifest the recipient can use
The proposed manifest below is a practical technical checklist. Adapt it to the recipient’s requirements and applicable handling policy.
| Manifest item | Useful content | Verification |
|---|---|---|
| Scope | Incident/reference ID, cameras and requested interval | Match authorization and selection |
| File inventory | Names, sizes, formats and roles | Confirm all expected files arrived |
| Time context | Recording interval, time zone and known offset | Compare display with source record |
| Integrity | Algorithm, values and verification event | Recompute against the trusted manifest |
| Playback | Software/version and test outcome | Open outside the original VMS |
| Derivatives | Conversion, redaction or annotation history | Keep preservation and viewing copies distinct |
| Custody/transfer | Authorized sender, recipient, time and method | Confirm receipt and responsibility |
Do not confuse the hash manifest with the entire chain of custody. People, transfers, permissions and handling events remain part of the record.
Control access after the file leaves the VMS
A downloaded copy no longer inherits every control of the recording platform. Use an approved transfer channel, limit recipients and apply the relevant retention or legal-hold process. Test that access restrictions do not make the package unusable for its authorized purpose.
Include a recipient-side export exercise in acceptance: the authorized recipient should be able to verify the package, open the files and interpret the timestamps and missing intervals.
FAQs
Does a matching file hash prove that a video depicts a real event?
No. A matching cryptographic hash can support a comparison of file contents against a trusted recorded value. It does not by itself establish when, where or how the video was captured, or whether the source was authentic.
Should a converted MP4 replace the original CCTV export?
No. Keep the preservation export and its associated files. A converted viewing copy should be separately identified, with the conversion and any changes recorded.
Why test video playback outside the recorder?
The recipient may not have the same software, codecs, licenses or network access. Independent playback testing exposes missing dependencies, lost time information and incomplete exports before handover.